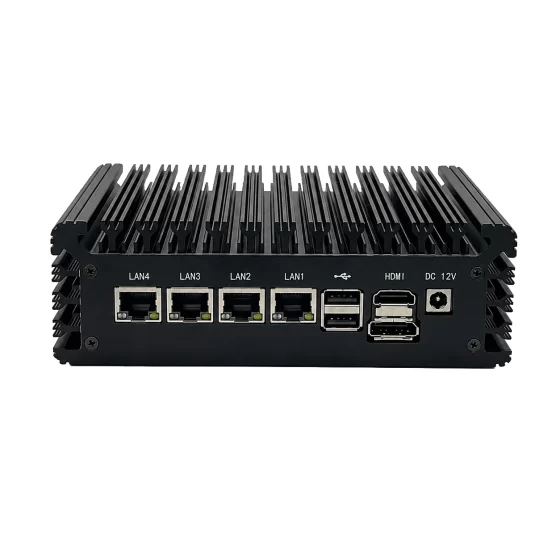
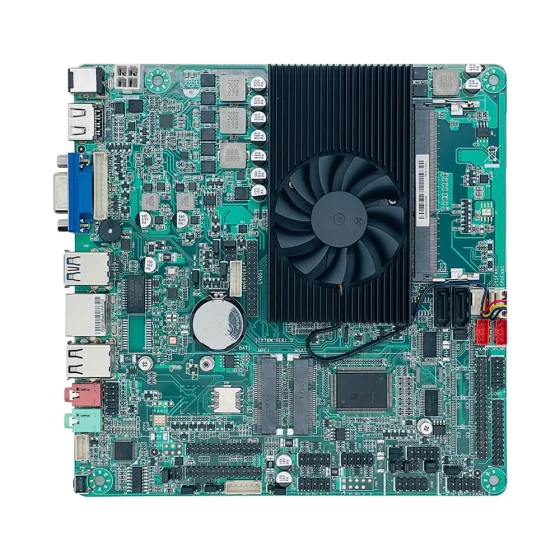
Решения CoreIPC для промышленных вычислений

Устройство безопасной связи: Устройство защищенной связи для подключения к промышленной сети
Управляющее резюме
A secure communications appliance provides the industrial computing foundation for encrypted data transfer, безопасный удаленный доступ, соединение между площадками, промышленная IoT-связь, сегментация сети, and protected communication between machines, field devices, пользователи, and higher-level platforms.
Современная промышленная среда становится все более взаимосвязанной. Заводы, склады, энергетические объекты, транспортные системы, удаленные объекты, and smart infrastructure networks now depend on PLCs, датчики, камеры, промышленные ПК, встроенные компьютеры, СКАДА-системы, IIoT-шлюзы, облачные платформы, and remote engineering tools.
This connectivity improves visibility and efficiency, but it also creates security risks.
Industrial systems may need to exchange data across different networks, удаленные сайты, облачные платформы, and service teams. If communication is not protected, sensitive operational data, remote access paths, and machine networks may become exposed.
A secure communications appliance built on an industrial computer or embedded computer can provide a controlled hardware platform for secure tunnels, VPN-подключение, encrypted data transfer, политики брандмауэра, локальная регистрация, certificate storage, контроль доступа, and reliable field deployment.
Compared with standard routers or office communication devices, industrial communication appliances must operate reliably inside cabinets, машины, удаленные объекты, транспортная инфраструктура, and harsh field environments.
This article explains how secure communications appliances support industrial connectivity, какие проблемы с развертыванием возникают в реальных приложениях, как работает архитектура решения, and which hardware features matter when selecting an industrial computer or embedded computer for secure communications appliance deployment.
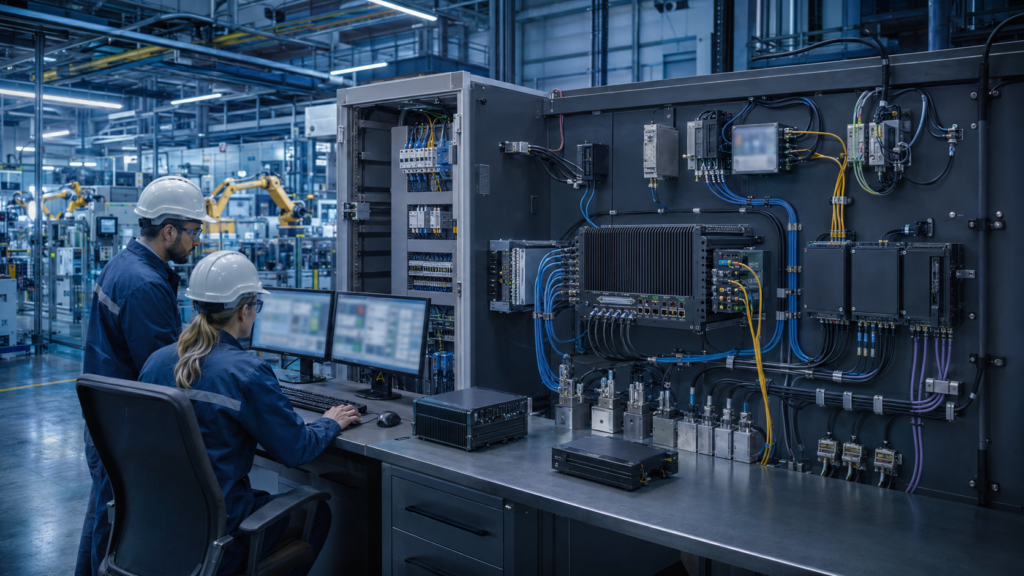
Secure Industrial Factory Connectivity
Обзор отрасли
Industrial Communication Is Becoming More Distributed
Industrial networks are no longer limited to one local control room.
Машины, контролеры, датчики, шлюзы, remote support tools, облачные информационные панели, and enterprise platforms now need to communicate across multiple locations.
Common communication needs include:
- Machine-to-platform data transfer
- Site-to-site industrial connectivity
- Удаленный доступ для обслуживания
- Удаленный мониторинг SCADA
- Загрузка данных промышленного Интернета вещей
- Secure cloud communication
- Соединение между заводом и центром обработки данных
- Удаленный мониторинг объекта
- Energy and utility data transfer
- Transportation infrastructure communication
- OEM equipment service connectivity
These communication paths must be protected because they often connect critical industrial assets with external systems.
Secure Communication Requires More Than Basic Routing
A basic router can move traffic between networks.
A secure communications appliance must do more.
В зависимости от конфигурации программного обеспечения, это может поддержать:
- Encrypted tunnels
- VPN-подключение
- Политики брандмауэра
- Сегментация сети
- Device authentication
- Certificate management
- Локальное ведение журнала
- Безопасный удаленный доступ
- Буферизация данных
- Link monitoring
- Контроль доступа
- Communication policy enforcement
This is important because industrial communication often includes operational data, состояние машины, сигналы тревоги, сеансы удаленного обслуживания, and production-related information.
Industrial Hardware Is the Reliable Foundation
Secure communications appliances may be deployed in production cabinets, машинные корпуса, подстанции, придорожные ящики, складские стеллажи, remote monitoring stations, and utility rooms.
These sites may include dust, вибрация, изменение температуры, нестабильная мощность, ограниченный поток воздуха, напряжение кабеля, и ограниченный доступ для обслуживания.
Industrial computers and embedded computers provide a stronger platform for these conditions.
Они поддерживают прочные корпуса, варианты безвентиляторной работы, сеть с несколькими локальными сетями, локальное хранилище, гибкий ввод-вывод, промышленный монтаж, и доступность в течение длительного жизненного цикла.

Secure Communications Deployment Challenges
Ключевые проблемы
Protecting Data Moving Across Networks
Industrial data may move between machines, шлюзы, СКАДА-системы, облачные информационные панели, enterprise platforms, and remote service teams.
If this communication is not protected, sensitive information may be exposed.
A secure communications appliance should help protect:
- Машинные данные
- Записи датчиков
- Тревожные сообщения
- Сеансы удаленного обслуживания
- SCADA-коммуникация
- Industrial IoT data
- Конфигурационные файлы
- Системные журналы
- Monitoring records
- Site-to-site data transfer
The appliance should support secure communication paths while keeping unnecessary access blocked.
Connecting Remote Sites Reliably
Many industrial systems are distributed across multiple sites.
A company may operate factories, склады, насосные станции, энергетические объекты, транспортные узлы, or customer-installed machines in different locations.
Each site may have different network quality and different maintenance conditions.
A secure communications appliance may need to support:
- Первичный восходящий канал WAN
- Backup WAN connection
- Cellular router integration
- Межсайтовый VPN
- Secure tunnel recovery
- Локальная буферизация данных
- Ссылка на мониторинг работоспособности
- Удаленная диагностика
Reliable communication is important when operators depend on remote visibility.
Separating Local Network Zones
Industrial communication appliances often sit between different networks.
They may need to separate machine networks, заводские ИТ-сети, industrial IoT networks, remote service networks, и сети управления.
A flat network increases risk.
A secure communications appliance may need to separate:
- Восходящий канал WAN
- Заводская ИТ-сеть
- Сеть ПЛК
- Машинная сеть
- СКАДА-сеть
- Сеть камер
- Промышленная сеть Интернета вещей
- Сеть удаленного обслуживания
- Сеть управления
Multiple LAN ports and clear policies help create controlled communication paths.
Supporting Legacy and Modern Systems
Industrial environments often include both modern and legacy equipment.
A secure communications appliance may need to connect Ethernet devices, последовательные устройства, промышленные шлюзы, датчики, local computers, remote platforms, и облачные сервисы.
Some devices may not support encryption or authentication directly.
The appliance can help provide protection at the network boundary.
It can secure communication paths without requiring every legacy device to be replaced immediately.
Maintaining Continuous Operation
Communication appliances can become critical infrastructure.
Если прибор вышел из строя, удаленный мониторинг, загрузка данных, site-to-site communication, or remote maintenance may stop.
Industrial deployment requires stable hardware.
К важным факторам надежности относятся:
- Безвентиляторный дизайн
- Прочный корпус
- Reliable storage
- Промышленная потребляемая мощность
- Стабильные тепловые характеристики
- Надежный монтаж
- Кабельная организация
- Удаленное управление
- Резервное копирование конфигурации
- Поддержка длительного жизненного цикла
The appliance must remain stable during continuous operation.

Secure Communications Appliance Architecture
Secure Communications Appliance Solution Architecture
Уровень полевых устройств
The field device layer includes the local systems that generate or receive data.
Этот слой может включать в себя:
- ПЛК
- HMI
- SCADA devices
- Датчики
- Счетчики энергии
- Промышленные камеры
- Роботы
- Контроллеры станков
- Встроенные контроллеры
- IIoT-шлюзы
- Локальные серверы
- Модули удаленного ввода-вывода
These devices may not all communicate directly with external platforms.
The secure communications appliance provides the controlled connection point.
Secure Communications Appliance Layer
The secure communications appliance layer is the core of the deployment.
На этом слое, промышленный компьютер или встроенный компьютер может:
- Создание зашифрованных туннелей
- Маршрут одобренного трафика
- Применить правила брандмауэра
- Сегментировать локальные сети
- Store certificates
- Buffer data locally
- Log communication events
- Поддержка удаленного доступа
- Monitor uplink status
- Connect to management platforms
This layer protects communication between local industrial assets and remote systems.
Уровень политики безопасности
The security policy layer defines which communication is allowed, ограниченный, encrypted, logged, or blocked.
Политика может быть основана на:
- Сетевая зона
- Группа устройств
- Роль пользователя
- Местоположение сайта
- Тип приложения
- Цель удаленного доступа
- Промышленный протокол
- Временное окно
- Security level
- Data type
Для промышленных сред, policies should be designed with both IT security teams and OT engineering teams.
This helps protect systems while maintaining required production communication.
Remote and Multi-Site Communication Layer
The remote communication layer connects field systems with external users and platforms.
Он может включать в себя:
- Межсайтовый VPN
- Удаленный доступ инженера
- OEM service tunnel
- Factory-to-cloud communication
- Удаленный мониторинг SCADA
- Передача данных промышленного Интернета вещей
- Branch-to-headquarters connection
- Remote facility access
- Maintenance platform connection
This layer allows distributed assets to communicate through controlled and secure channels.
Уровень мониторинга и управления
Secure communication requires visibility.
Устройство может предоставлять локальные информационные панели., удаленный мониторинг, журналы, статус ссылки, статус туннеля, and device health data.
Полезная информация мониторинга может включать:
- Статус туннеля
- WAN link health
- Remote access records
- Blocked traffic logs
- Data transfer history
- Certificate status
- Использование процессора и памяти
- Статус хранилища
- Температура устройства
- Изменения конфигурации
This information supports troubleshooting, аудиторская проверка, and long-term communication reliability.
Ключевые особенности
Сегментация сети из нескольких локальных сетей
Multiple LAN ports are important for secure communications appliances.
They allow the platform to separate local networks and define controlled traffic paths.
Полезные конфигурации могут включать в себя:
- Восходящий канал WAN
- Резервный восходящий канал WAN
- Заводская ИТ-сеть
- Сеть ПЛК
- Машинная сеть
- СКАДА-сеть
- Сеть камер
- Промышленная сеть Интернета вещей
- Сеть удаленного обслуживания
Конструкция с несколькими локальными сетями повышает безопасность, ясность маршрутизации, and deployment flexibility.
Encrypted Communication Performance
A secure communications appliance may process encrypted tunnels, VPN traffic, правила маршрутизации, политики брандмауэра, and data transfer workloads.
При выборе оборудования следует учитывать:
- Производительность процессора
- Объем памяти
- Количество портов локальной сети
- Скорость порта
- Количество туннелей
- Зашифрованная пропускная способность
- Рабочая нагрузка брандмауэра
- Объем журнала
- Скорость хранения
- Поддержка операционной системы
Для более крупных развертываний на нескольких площадках, the system should be tested with realistic traffic.
VPN and Secure Tunnel Support
Secure tunnel capability is a key function.
The appliance may support remote maintenance, site-to-site communication, cloud connection, or private industrial network links.
Tunnel design should consider:
- Number of remote sites
- User count
- Encryption workload
- Authentication method
- Хранение сертификатов
- Failover behavior
- Требования к ведению журнала
- Recovery procedures
Secure tunnel design helps protect communication between distributed industrial systems.
Надежное локальное хранилище
Локальное хранилище поддерживает системные файлы, сертификаты, резервные копии конфигурации, журналы, записи событий, диагностические файлы, and data buffers.
Обычно предпочтение отдается твердотельным накопителям или хранилищам NVMe, поскольку они обеспечивают быстрый доступ и лучшую ударопрочность, чем механические накопители..
При планировании хранения следует учитывать:
- Хранение журнала
- Хранение сертификатов
- Резервное копирование конфигурации
- Локальная буферизация данных
- Восстановление системы
- Записи событий безопасности
- Напишите выносливость
- Рабочий процесс резервного копирования
Reliable storage improves communication continuity and auditability.
Буферизация данных и промежуточное хранение
Some remote sites may experience unstable network connectivity.
A secure communications appliance can buffer data locally and forward it when the connection recovers.
Это полезно для:
- Remote monitoring sites
- Энергетические объекты
- Транспортная инфраструктура
- Промышленные системы Интернета вещей
- Экологический мониторинг
- SCADA data collection
- Machine status reporting
Store-and-forward capability helps reduce data loss during temporary network interruptions.
Прочная и безвентиляторная конструкция
Fanless industrial computers are useful for communication appliances deployed in dusty cabinets and remote environments.
Они уменьшают попадание пыли и устраняют одну распространенную точку механического отказа..
Прочные корпуса защищают от вибрации, монтажное напряжение, напряжение кабеля, и непрерывная работа.
Thermal design should still be reviewed carefully because encryption, маршрутизация, and logging can create sustained workload.
Гибкий промышленный ввод-вывод
Secure communication platforms may need to connect more than Ethernet devices.
Полезные параметры ввода-вывода могут включать в себя:
- локальная сеть
- USB
- RS232
- RS485
- GPIO
- Цифровой вход
- Цифровой выход
- HDMI
- ДисплейПорт
- М.2
- PCIe
- SATA или NVMe
Serial ports can support legacy industrial equipment. GPIO can support alarm signals. Варианты расширения могут поддерживать беспроводные модули., дополнительные LAN-порты, или устройства хранения.
Длительный жизненный цикл и ремонтопригодность
Secure communications appliances may remain in service for many years.
Согласованное оборудование помогает поддерживать образы программного обеспечения, security configurations, совместимость драйверов, планирование запасных частей, и проверка.
Industrial computing platforms with lifecycle planning help system integrators and operators deploy stable communication appliances across multiple sites and equipment generations.

Secure Industrial Communications Operations
Сценарии развертывания
Remote Machine Communication
Machine builders can use secure communications appliances to connect equipment at customer sites with remote service platforms.
The appliance can establish secure tunnels, control access, хранить журналы, and support diagnostics.
This helps OEMs provide service while reducing broad network exposure.
Factory-to-Cloud Communication
Factories may need to send selected data to cloud dashboards or industrial IoT platforms.
A secure communications appliance can encrypt communication, filter data, сегментировать машинные сети, and log data transfer events.
This supports safer connected manufacturing.
Site-to-Site Industrial Connectivity
Multi-site industrial operators may need secure communication between factories, склады, удаленные объекты, и дата-центры.
The appliance can support site-to-site VPN tunnels, traffic policies, and local monitoring.
This improves connectivity across distributed operations.
SCADA Remote Communication
Системы SCADA часто соединяют диспетчерские, удаленные устройства, field equipment, и центры мониторинга.
A secure communications appliance can protect remote SCADA communication and provide controlled access paths.
Это полезно для энергии, вода, транспорт, и инфраструктура объекта.
Industrial IoT Data Transfer
Industrial IoT systems depend on reliable data transfer between machines, датчики, шлюзы, and platforms.
A secure communications appliance can support encrypted data upload, локальная буферизация, gateway protection, и сегментация сети.
This improves IIoT communication reliability and security.
Warehouse and Logistics Connectivity
Warehouses may include automation systems, станции штрих-кода, камеры, конвейеры, промышленные компьютеры, и WMS-платформы.
A secure communications appliance can connect local systems with enterprise or cloud platforms while maintaining local network separation.
Это поддерживает безопасные логистические операции..
Transportation Infrastructure Communication
Транспортные системы могут включать в себя придорожное оборудование., регулировщики, парковочные системы, станции, и центры мониторинга.
A secure communications appliance can support protected communication between distributed infrastructure nodes and central management platforms.
OEM Secure Communication Appliance Development
System integrators and equipment builders can build custom secure communication appliances using industrial computers or embedded boards.
The platform can support secure tunnels, сеть с несколькими локальными сетями, маршрутизация, локальное хранилище, регистрация, удаленное управление, и надежное развертывание.
Преимущества для бизнеса
Protected Industrial Data Transfer
A secure communications appliance helps protect data moving between machines, сайты, пользователи, and platforms.
Encrypted communication, политики доступа, and logging reduce the risk of uncontrolled data exposure.
This is important for connected factories and distributed infrastructure.
Более безопасное удаленное обслуживание
Удаленное обслуживание может сократить время простоя и затраты на поддержку..
A secure communications appliance helps control remote access through approved tunnels, политики доступа, and logs.
Authorized engineers can connect to required systems without exposing the full industrial network.
Better Network Segmentation
Multi-LAN appliances help separate factory IT, ОТ, машина, камера, IIoT, удаленное обслуживание, и сети управления.
This reduces unnecessary exposure and improves network clarity.
Segmentation is especially important when communication paths connect local systems with external platforms.
Improved Communication Reliability
Локальная буферизация, мониторинг ссылок, and rugged hardware help keep communication stable.
Remote sites can continue collecting data during temporary network interruptions and forward records later.
This improves operational continuity for distributed industrial systems.
Stronger Auditability
Secure communications appliances can store access records, tunnel logs, заблокированные дорожные события, configuration changes, and system health records.
These logs support troubleshooting, аудиторская проверка, расследование безопасности, и долгосрочное обслуживание.
Reliable local storage improves traceability.
Scalable Secure Connectivity
A standardized secure communications appliance platform makes it easier to deploy across many machines, удобства, филиалы, и удаленные сайты.
Согласованное оборудование упрощает образы программного обеспечения, security templates, планирование запасных частей, удаленное обслуживание, и управление жизненным циклом.
This supports scalable industrial connectivity programs.
Почему CoreIPC
CoreIPC предоставляет промышленные вычислительные платформы для сетевой безопасности, промышленный Интернет вещей, удаленный мониторинг, умный транспорт, энергетический менеджмент, и встроенная системная интеграция. For secure communications appliance applications, CoreIPC специализируется на надежном промышленном компьютерном оборудовании., встроенные компьютерные решения, конфигурации с несколькими локальными сетями, гибкий ввод-вывод, компактная конструкция системы, варианты безвентиляторного развертывания, возможность локального хранения, и поддержка настройки OEM/ODM. CoreIPC помогает системным интеграторам, производители оборудования, и промышленные операторы выбирают вычислительные платформы, соответствующие реальным требованиям развертывания, включая количество портов LAN, tunnel workload, encryption performance, сегментация сети, потребности в хранении, способы крепления, потребляемая мощность, термические условия, и планирование жизненного цикла.
Часто задаваемые вопросы
1. What is a secure communications appliance?
A secure communications appliance is a hardware platform used to protect communication between local industrial devices, удаленные пользователи, сайты, облачные платформы, и корпоративные системы.
It may support encrypted tunnels, VPN, политики брандмауэра, контроль доступа, регистрация, local data buffering, сегментация сети, and secure remote maintenance.
2. Why use an industrial computer for a secure communications appliance?
Промышленный компьютер обеспечивает надежное оборудование и гибкие возможности подключения для развертывания на заводе и в полевых условиях..
Он может поддерживать несколько портов LAN., надежное хранение, безвентиляторный режим, промышленный монтаж, стабильная потребляемая мощность, и доступность в течение длительного жизненного цикла. These features make it suitable for communication appliances installed in cabinets, машины, удаленные объекты, и инфраструктурные объекты.
3. How is an embedded computer used as a secure communication platform?
An embedded computer can act as a compact secure communication gateway inside a machine enclosure, шкаф управления, удаленный объект, or OEM appliance.
It can run VPN, маршрутизация, регистрация, tunnel management, буферизация данных, and network segmentation software while providing a compact footprint.
4. What is the difference between a secure communications appliance and a router?
A router mainly forwards traffic between networks.
A secure communications appliance adds protection functions such as encryption, VPN, политики брандмауэра, контроль доступа, регистрация, certificate storage, буферизация данных, and controlled remote access. This makes it more suitable for connected industrial systems.
5. Why are multiple LAN ports important for secure communications appliances?
Несколько портов LAN позволяют устройству разделять разные сетевые зоны..
Один порт может подключаться к WAN, другой для заводского ИТ, другой для сетей ПЛК, другой для машинных сетей, а другой — для удаленного обслуживания или промышленных систем Интернета вещей.. This supports controlled communication and stronger segmentation.
6. Can fanless industrial computers support secure communication workloads?
Да. Fanless industrial computers can support many secure communications appliance deployments because they reduce dust intake and remove one mechanical failure point.
Однако, зашифрованные туннели, VPN traffic, маршрутизация, регистрация, and local buffering can create sustained workload. Производительность процессора, конструкция корпуса, температура окружающей среды, и поток воздуха в шкафу следует проверить перед развертыванием.
7. What hardware features matter for secure communications appliances?
Важные функции включают несколько портов LAN., достаточная производительность процессора, надежная память, SSD или NVMe-хранилище, прочный корпус, безвентиляторный дизайн, промышленная потребляемая мощность, USB, последовательные порты, GPIO, вывод дисплея, и возможности расширения.
Окончательная конфигурация должна соответствовать количеству туннелей., объем трафика, потребности в хранении, сетевые зоны, и среда установки.
8. Can secure communications appliances support industrial IoT?
Да. Secure communications appliances can support industrial IoT by protecting data transfer between machines, датчики, шлюзы, облачные платформы, и системы мониторинга.
They can also buffer data, segment local networks, and control external communication paths.
9. Can a secure communications appliance support remote maintenance?
Да. It can support remote maintenance through VPN or secure tunnels, access control policies, session logging, и сегментация сети.
This allows authorized engineers to connect to required systems while limiting unnecessary exposure to other industrial assets.
10. Что следует протестировать перед развертыванием?
Перед развертыванием, система должна быть протестирована с реальной топологией сети, количество туннелей, Рабочая нагрузка VPN, объем трафика, политики брандмауэра, data buffering behavior, регистрация рабочей нагрузки, и длительная эксплуатация.
Термическая стабильность, link recovery, резервное копирование конфигурации, рабочий процесс удаленного доступа, и производственная коммуникация также должна быть проверена.
Заключение
A secure communications appliance is a practical foundation for encrypted industrial data transfer, безопасный удаленный доступ, соединение между площадками, промышленная IoT-связь, сегментация сети, and protected communication across distributed systems.
By placing an industrial computer or embedded computer at key communication boundaries, производители, машиностроители, системные интеграторы, и операторы инфраструктуры могут подключать ПЛК, датчики, машины, СКАДА-системы, облачные платформы, удаленные объекты, and service teams through controlled and secure paths.
The right secure communications appliance should be selected according to real deployment requirements, включая количество портов LAN, tunnel workload, зашифрованная пропускная способность, объем трафика, потребности в хранении, data buffering requirements, метод монтажа, потребляемая мощность, термические условия, поддержка операционной системы, политика безопасности, и планирование жизненного цикла.
CoreIPC supports secure communications appliance projects with industrial computing platforms designed for practical factory, машинная сторона, ветвь, и развертывание на местах. С правильной аппаратной основой, промышленные операторы и производители оборудования могут создавать надежные, масштабируемый, and secure communication systems.
Связаться с нами
Ищу промышленный компьютер, встроенный компьютер, or multi-LAN platform for secure communications appliance deployment?
Свяжитесь с CoreIPC, чтобы обсудить требования вашего проекта, включая количество портов LAN, secure tunnel workload, encryption performance, сегментация сети, конфигурация хранилища, метод монтажа, потребляемая мощность, операционная среда, потребности жизненного цикла, и варианты настройки OEM/ODM.